Account owner authorization
Only the owner of a seller account or advertising account can authorize KEYXE, on Amazon’s own consent screen. KEYXE never collects Amazon passwords.
KEYXE Security & Permissions
Access to a seller account is not the same as access to an advertising account. KEYXE treats each permission as an explicit choice and designs auditability into the workflow.
Design controls
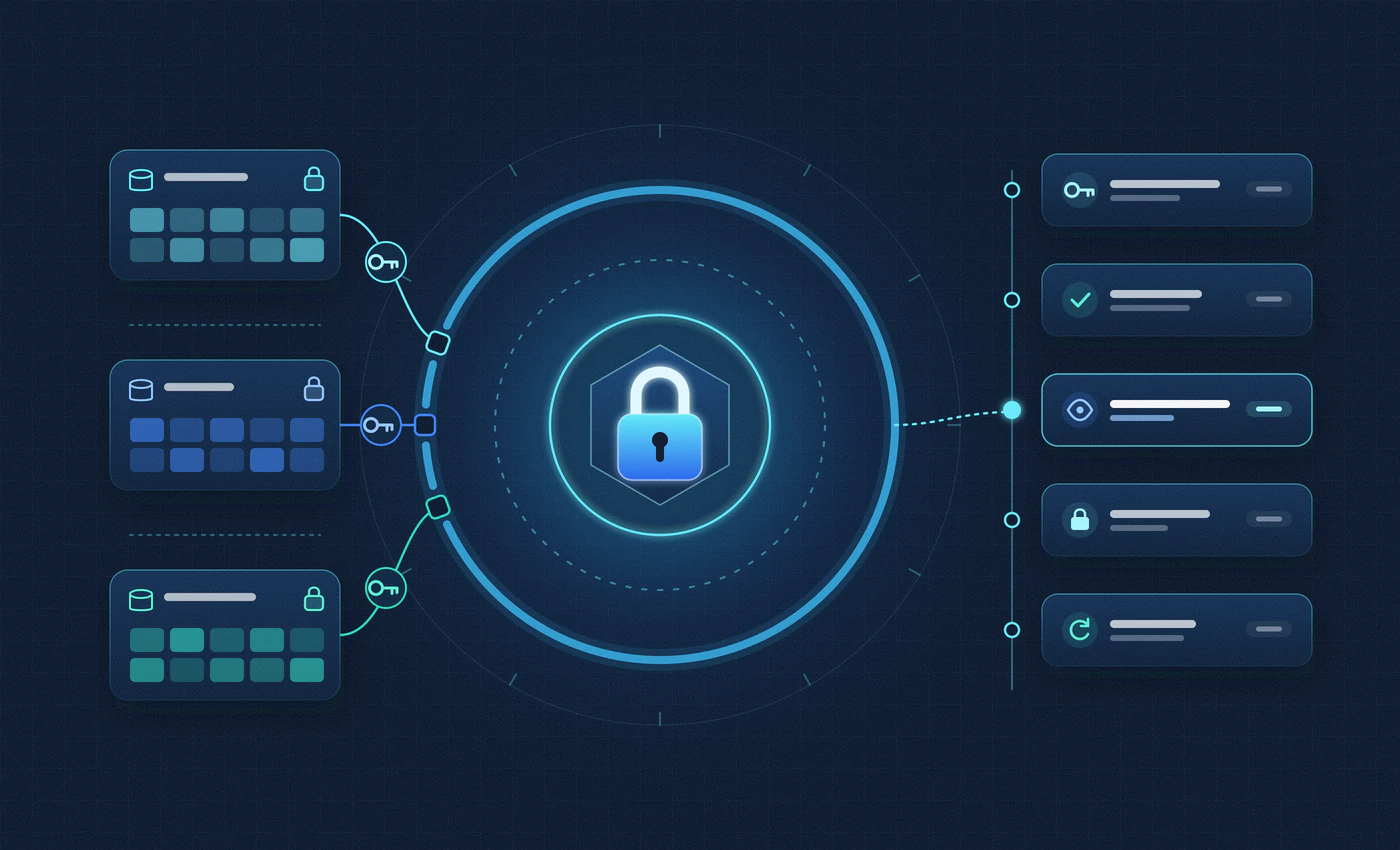
These are the design rules for live Amazon integrations, which are not available yet. Today they shape the demo and the disabled Amazon routes in the KEYXE API.
Only the owner of a seller account or advertising account can authorize KEYXE, on Amazon’s own consent screen. KEYXE never collects Amazon passwords.
KEYXE requests only the roles and scopes a customer-facing workflow needs. Restricted buyer data is not part of the planned scope.
Each organization’s connections, reports and settings are separated, and every request is checked against the organization it belongs to.
Seller access and advertising access are revoked separately. Revoking one never silently affects the other.
Sign-ins, connection changes, exports and reviewed proposals are designed to be logged with who, what and when.
Any future account-changing action requires explicit permission, a preview of the change and a person’s approval. Nothing runs unattended.
Example
Viewer, Analyst and Admin are synthetic example roles. They show the intended model — they are not proof that a production role system exists today.
| Ability | Viewer | Analyst | Admin | Availability |
|---|---|---|---|---|
| View demo dashboards | Allowed | Allowed | Allowed | Demo only |
| Export synthetic report | Not allowed | Allowed | Allowed | Demo only |
| Draft a reviewable proposal | Not allowed | Allowed | Allowed | Demo only |
| Approve account change | Not allowed | Not allowed | Allowed | Planned — not available |
| Connect or revoke an Amazon account | Not allowed | Not allowed | Allowed | Requires Amazon approval |
The public demo has no sign-in and no roles — everyone sees the same synthetic data. A role-based production system will be described here only once it exists and has been tested.
Three separate authorizations
The Security page separates safeguards running on this website from controls planned for live integrations.